Best Network Security Monitoring Services: 24/7 Protection for Companies
Explore network security monitoring services that provide 24/7 threat detection, real-time monitoring, incident response, and proactive protection to help businesses secure their IT infrastructure.
23
Sep
Best Network Security Monitoring Services: 24/7 Protection for Companies
Published 23 Sep 2026 Updated 23 Sep 2026 Written and reviewed by Anshul Goyal
Table of Contents
- What Are Network Security Monitoring Services?
- Why Do Companies Need 24/7 Monitoring?
- What Should Be Monitored?
- 24/7 Security Monitoring Options
- MSSP vs MDR vs Co-Managed SOC
- How Network Security Monitoring Works
- Benefits of Network Security Monitoring
- How to Select a Provider
- Frequently Asked Questions
- Conclusion
Network security monitoring services ensure comprehensive security by analyzing activity in a company’s networks, endpoints, cloud systems, user identities and security logs.
Analysts and security technology are combined to offer detection and response to threats, and investigation of alerts before incidents are able to inflict damage. Organizations are able to select among in-house SOC, MSSP, MDR, provider, co-managed SOC and cloud-based monitoring.
Which selection is the best option varies by the size of the business, the security and threat risk the organization faces, the expertise present in the organization, the compliance and the expected time to respond.
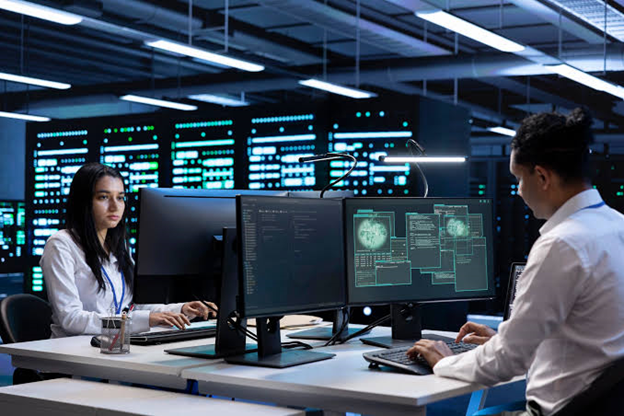
What Are Network Security Monitoring Services?
Continuous collection and analysis of network activity and security data to provide optimal network security involves the following:
-
1. Malware and ransomware
-
2. Unauthorized access
-
3. Suspicious log-in attempts
-
4. Compromised accounts
-
5. Unusual data transfers/malicious networks
-
6. Security policy violations
-
7. Connections to critical systems
Security monitoring services are still comprehensive and include the following:
-
1. SIEM monitoring
-
2. Endpoint detection and response
-
3. Network analysis
-
4. Intrusion detection monitoring
-
5. Cloud security monitoring
-
6. Identity threat detection
-
7. Threat intelligence
-
8. Human alert investigation
-
9. Threat containment
-
10. Compliance reporting
Unlike regular network monitoring, which focuses on uptime and performance, network security monitoring focuses on malicious or unauthorized activities.
Why Do Companies Need 24/7 Monitoring?
Cyberattacks can be difficult to detect because they may be carried outside of business hours. Attackers may target systems overnight, on the weekends, or during holidays because internal teams are not available then.
Automated security tools can generate alerts. However, those alerts lose their value if no one is there to investigate them.
Continuous security monitoring means that the following are maintained:
-
1. An always working system that collects data
-
2. Automated detection of threats
-
3. People to evaluate alerts that are generated
-
4. Escalation procedures that are known and defined
-
5. Contacts that are customers and are always available
-
6. Assistance to support the containment of threats
-
7. Response times and commitments that are defined
-
8. Incidents and how they are resolved documented in detail
Companies have to decide if a provider really staffed their SOC and is monitoring it 24/7 or if they only have an automated alerting system.
What Should Be Monitored?
A modern security monitoring service should cover more than firewalls.
Important data sources include:
|
Data Source |
Possible Threats Detected |
|
Firewalls and gateways |
Malicious connections and blocked traffic |
|
Endpoints and servers |
Malware and suspicious processes |
|
Identity platforms |
Account compromise and privilege abuse |
|
Cloud systems |
Configuration changes and unusual API activity |
|
Email security |
Phishing and malicious attachments |
|
VPN systems |
Suspicious remote access |
|
DNS logs |
Connections to malicious domains |
|
Business applications |
Unusual access to sensitive records |
|
Backup systems |
Ransomware-related deletion attempts |
|
Third-party connections |
Supplier or external-account compromise |
The service can only detect activity from systems that are properly connected and monitored. Missing logs create security blind spots.
24/7 Security Monitoring Options
1. In-House SOC
An in-house security operations centre is run by an enterprise’s own security analysts and incident responders.
Best for: Large scale enterprises and very highly regulated enterprises.
Advantages:
-
1. Complete control
-
2. Strong knowledge of the business
-
3. Ability to create custom detection rules
-
4. Direct access to business systems
Limitations:
-
1. Very high staffing costs
-
2. Hard to maintain a 24/7 security operations team
-
3. Responsible for maintaining the tools
-
4. Staff turnover and analyst fatigue
2. Managed Security Service Provider
An MSSP handles security tools, monitors logs, and alerts the business when potentially harmful activities are detected.
Best for: Small and mid-sized businesses that require handled security monitoring.
MSSPs could monitor firewalls, SIEM alerts, security concerns, and other security tools. That said, some send alerts and do not take action against threats.
3. Managed Detection and Response
MDR is the combination of security technology and human investigations, threat hunting, and response activities.
Depending on the contract, an MDR vendor could:
-
1. Identify and lock networks of threat actors and malicious devices
-
2. Restricted access of compromised accounts
-
3. Suspicious sessions revoked
-
4. Assisted forensics and recovery of incidents
Best for: Businesses that require fast investigation and response but do not have developed in-house SOC capabilities.
4. Co-Managed SOC
A co-managed SOC is the combination of a business’s internal security knowledge and external analysts and SOC capabilities.
The external vendor could take care of monitoring and investigations while the internal team takes care of critical business decisions.
Best for: Businesses that have a limited security team and require additional coverage and security expertise.
5. Cloud-Native Monitoring
Cloud-native monitoring is the combination of built-in security tools in cloud platforms and SaaS applications.
Best for: Start-ups and businesses that focus on the cloud.
While cloud tools can offer valuable threat detection, they still need the correct rules to be configured, as well as skills for investigation and response.
MSSP vs MDR vs Co-Managed SOC
|
Option |
Main Focus |
Response Level |
Best Fit |
|
MSSP |
Monitoring and alert management |
Low to moderate |
SMBs needing managed security |
|
MDR |
Investigation and containment |
High |
Companies needing active response |
|
Co-managed SOC |
Shared monitoring and response |
High |
Businesses with internal security staff |
|
In-house SOC |
Complete internal control |
High |
Large enterprises |
|
Cloud-native |
Platform-based monitoring |
Variable |
Cloud-first companies |
In simple terms, an MSSP mainly monitors, MDR investigates and responds, while a co-managed SOC shares responsibilities with the internal team.
How Network Security Monitoring Works
1. Identify Critical Assets
The important systems, users, applications, data, and third-party services have been identified by the company.
2. Connect Security Data
Data from endpoints, firewalls, cloud apps, identity, and email and business apps is sent to a central security monitoring system.
3. Detect Suspicious Activity
Security systems detect abnormal activities like the following.
-
1. Multiple failed login attempts
-
2. New admin accounts
-
3. Unexpected network activities
-
4. Malware begin to run
-
5. Large amounts of data are copied
-
6. Security is bypassed
-
7. Access is from a location that is not normal
4. Investigate the Alert
Security analysts investigate the alert by looking at the user, device, activities of the users, and the impacted systems.
5. Contain the Threat
Isolation of the device, blocking the domain, disabling the account, and revoking access credentials are all actions that are approved.
6. Report and Improve
Incidents are logged, and the rules for detection are amended so that a similar type of attack will not be able to succeed.
Important Capabilities to Look For
A dependable service will offer:
-
1. Real 24/7 Analyst Coverage
-
2. SIEM and EDR Connections
-
3. Monitoring for Network, Cloud and Identity
-
4. Enrichment via Threat Intelligence
-
5. Investigations Conducted by Humans
-
6. Threat Searching
-
7. Levels of Incident Severity
-
8. Response Time Goals
-
9. Escalation Procedures Custom to Client
-
10. Retention of Logs in a Secure Manner
-
11. Tuning of Detection, Regular
-
12. Reporting of Incidents
-
13. Support with Compliance
Potential clients should also ensure that the service is capable of acting autonomously rather than waiting for client approval.
Benefits of Network Security Monitoring
1. Enhanced Threat Detection
Before suspicious behaviors have the opportunity to escalate into significant threats, they are detected.
2. Less Alert Fatigue
The system sorts and manages alerts to global standards, filtering the low threats and elevating the real threats.
3. Availability of Security Experts
Clients can utilize security analysts and incident response teams without the need to build their own security teams.
4. Better Evidence for Incidents
Central records can show what happened, which systems were affected, and what responses were executed.
5. Higher Likelihood of Compliance
Retention of logs and records of incidents and responses can help during an audit and meet a regulatory standard.
Limitations
While network security monitoring reduces risk, challenges will most likely remain.
Below are some risks:
-
1. Lacking some log sources
-
2. Net devices that can't be managed
-
3. Frivolous alerts
-
4. Visibility into encrypted traffic
-
5. Slack response approvals
-
6. Issues with integration
-
7. Log-storage costs
-
8. Older systems that can’t be seen
Risk can’t be fully eliminated and thus, managing your assets, patching your software, employee education, backups and controlling who has access are still vital to security.
How to Select a Provider
Before choosing a service, ask:
-
1. Are there trained analysts who are available 24/7?
-
2. What systems and security tools do they support?
-
3. How quickly are critical alerts responded to?
-
4. Can the provider isolate devices or disable accounts?
-
5. Where would my security logs be stored?
-
6. How long would the logs be kept?
-
7. Is threat hunting and incident response part of the service?
-
8. What kind of reporting will be provided?
-
9. How does pricing change based on the number of users, endpoints, or the volume of logs?
-
10. Will the provider be able to run a pilot or proof of value?
Don't select a provider just because they support a lot of tools. Prioritize investigation quality, response authority, and verifiable service commitments.
Frequently Asked Questions
1. What is 24/7 network security monitoring?
This is when security systems and qualified analysts monitor company activity all day, every day, all year round.
2. What is the difference between MSSP and MDR?
An MSSP uses analyst tools and monitors alerts. On the other hand, MDR does investigations, threat hunting, and offers an active response.
3. Does a small business need security monitoring?
Any small business can benefit from security monitoring, especially if a business has customer information, uses cloud apps, engages in online payments, and if the business cannot hire full-time security analysts.
4. Is SIEM the same as security monitoring?
No. SIEM is a tool to gather and combine security events, whereas security monitoring is analyst work to investigate, escalate, and respond to incidents.
5. Can monitoring stop ransomware?
No. Monitoring can help notice suspicious activity related to ransomware and help isolate the affected systems, however, it needs to be combined with regular patches, endpoint protection, access controls, and verified backups.
Conclusion
Network security monitoring services never let their guard down across networks, cloud systems and applications, looking for threats to security that could target employees, endpoints and the business.
MSSPs could work for companies that need less intensive managed monitoring, while organizations that need investigative response features and containment actively done require MDR. A co-managed SOC would be an option for companies that want to give their internal security team some extra support.
The ideal option should provide the support of analysts on a 24/7 basis, measurement, response and containment that is scoped, and reliable integrations.
Identify your current monitoring blind spots before selecting a service.
Start with a network security assessment to determine which systems require monitoring and whether MSSP, MDR or co-managed SOC protection is the best fit for your business.

Anshul Goyal
Group BDM at B M Infotrade | 11+ years Experience | Business Consultancy | Providing solutions in Cyber Security, Data Analytics, Cloud Computing, Digitization, Data and AI | IT Sales Leader